Security Ninja Premium
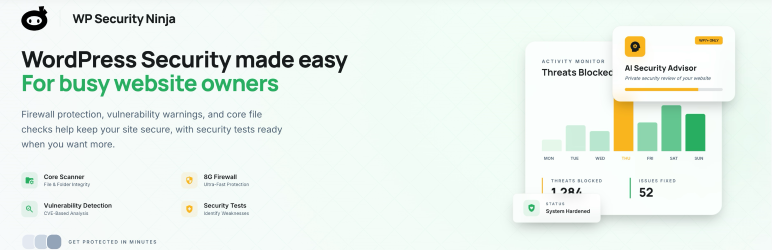
Security Ninja Premium is a proactive security management suite designed to protect WordPress websites from unauthorized access, malware infections, brute force attempts, and zero-day exploits. Operating with a clean, low-overhead architecture, it conducts over 50 comprehensive security tests—including database permission checks, file integrity scans, password strength evaluations, and header security audits—giving administrators actionable steps to fix vulnerabilities before hackers exploit them. The Premium tier enhances basic auditing with a dynamic Web Application Firewall (WAF), real-time file change monitoring, auto-blocking for malicious IP addresses, auto-fixing security holes, and an event logger to monitor all user activity across the dashboard.
Main Features
- 50+ comprehensive security tests — Audits core files, database tables, PHP settings, file permissions, security headers, and password policies for hidden vulnerabilities.
- Auto-fix module — Applies instant single-click patches and fixes for identified vulnerabilities without requiring code adjustments.
- Core & file integrity scanner — Compares active WordPress core files, plugins, and themes against official checksum repositories to detect unauthorized code modifications or backdoors.
- Cloud Web Application Firewall (WAF) — Filters incoming web traffic in real time, automatically blocking known malicious bots, exploit scanners, and brute-force login attacks.
- Detailed event logger — Tracks and records every action taken on your site (e.g., user logins, plugin activations, content edits, option updates, and failed access attempts).
- Vulnerability scanner for plugins & themes — Checks installed extensions against an updated database of known CVE vulnerabilities and warns webmasters of insecure plugins.
- Scheduled automatic security scans — Runs background vulnerability checks at user-defined intervals and delivers detailed email alerts when risks are discovered.
- IP ban & country blocking management — Manually or automatically blacklist offending IP ranges, suspicious user agents, or specific geographic regions.
Benefits
- Proactive threat protection — Identifies and resolves configuration flaws before attackers can leverage them for exploits.
- Low server resource consumption — Operates cleanly without running heavy, continuous background loops that slow down site performance.
- Complete administrative transparency — Detailed event logs give site managers full oversight of all user actions and security events.
- Protects site reputation & SEO — Prevents unauthorized redirects, SEO spam injections, and blacklist placement on search engines.
- Simple, actionable reporting — Explains security issues in clear, plain language accompanied by straightforward instructions or one-click fixes.
Who is it suitable for?
- WordPress site administrators & business owners seeking a clear, non-technical overview of site security vulnerabilities.
- WooCommerce store owners needing to protect customer privacy, user accounts, and financial transactions from brute-force or injection attacks.
- WordPress developers & agencies securing client websites and tracking administrative user activities across multi-author sites.
- High-traffic blogs & news networks requiring real-time firewall protection against automated botnets and malicious exploit scans.
## Bug Fixes
- REST API Authentication Handling: Resolved an edge-case conflict where strict firewall rule enforcement occasionally blocked legitimate external REST API application requests.
- Firewall State Persistence: Fixed a synchronization bug where custom Cloud Firewall configuration toggles intermittently reverted after bulk plugin updates.
- Change Login URL Persistence: Corrected an issue where customized login slug redirection rules failed to save correctly under specific multi-site permalink configurations.
security-ninja-premium.5.306.zip
0 reviews
You need to log in and purchase this product to leave a review.
LoginNo reviews yet
Be the first to review this product!